Feeds last updated @: UTC - 12:15 - 13/10/2026
Read more of this story at Slashdot.
https://www.theregister.com/security
https://hackread.com/mssps-strengthens-threat-hunting-against-ransomware/
https://hackread.com/amazon-fire-tv-cube-rooted-arm-mali-vulnerability/
https://hackread.com/g2a-com-reports-35-growth-in-security-software-orders-outpacing-vpn-growth/
https://hackread.com/why-vps-hosting-helps-openclaw-run-faster-reliably/
https://hackread.com/hackers-heat-supermarket-fridges-50c-france-cyberattack/
https://www.debian.org/security/
https://msrc.microsoft.com/update-guide/vulnerability
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-12429
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-12428
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-12727
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-12433
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-12441
https://www.ncsc.nl/alerts/kwetsbaarheden-in-hpe-networking-aos-switch-met-hoog-risico
https://www.ncsc.nl/alerts/meerdere-kwetsbaarheden-in-android-en-samsung-mobile-apparaten-update-nu
https://www.ncsc.nl/nieuws/veiligheidsdiensten-verwachten-toename-chinese-cyberaanvallen
https://www.ncsc.nl/alerts/kwetsbaarheid-in-microsoft-exchange-server-met-risico-op-misbruik
https://wid.cert-bund.de/portal/wid/securityadvisory?name=WID-SEC-2026-3891
https://wid.cert-bund.de/portal/wid/securityadvisory?name=WID-SEC-2026-3332
https://wid.cert-bund.de/portal/wid/securityadvisory?name=WID-SEC-2026-3619
https://wid.cert-bund.de/portal/wid/securityadvisory?name=WID-SEC-2026-3612
https://wid.cert-bund.de/portal/wid/securityadvisory?name=WID-SEC-2026-3444
https://thehackernews.com/2026/10/lg-smart-tvs-vulnerable-to-pre-auth.html
https://thehackernews.com/2026/10/product-walkthrough-bitdefender-ai.html
https://thehackernews.com/2026/10/attackers-heat-french-supermarket.html
https://thehackernews.com/2026/10/two-critical-marklogic-flaws-could-give.html
https://thehackernews.com/2026/10/gitlab-patches-cvss-100-flaw-that-could.html
https://techrepublic.com/topic/security
UK researchers regain access to advanced AI models for safety testing as ministers consider stronger incident reporting and expand government cyber defenses.
The post UK Regains Early Access to AI Models After Reported White House Reversal appeared first on TechRepublic.
https://www.techrepublic.com/article/news-uk-ai-model-access-white-house-reversal-emea/
Google has announced new Android Enterprise policies for controlling AI automation, alongside stronger work-profile protections and additional device-management features.
The post Google Adds Android Enterprise AI Controls: What IT Teams Can Manage appeared first on TechRepublic.
https://www.techrepublic.com/article/news-google-android-enterprise-ai-controls/
Explore the latest tech news, from ChatGPT's interactive AI tools and Microsoft's new hardware to cybersecurity threats, robotics, and Big Tech shakeups.
The post AI Agents, Local Hardware, and Security Risks Reshape Tech appeared first on TechRepublic.
https://www.techrepublic.com/article/ai-agents-local-hardware-and-security-risks-reshape-tech/
Five states have sued TP-Link over router security and disclosure claims. Here's how the lawsuits, FCC restrictions, and firmware vulnerabilities affect existing owners.
The post TP-Link Faces 5 State Lawsuits: Are Its Routers Still Legal in the US? appeared first on TechRepublic.
https://www.techrepublic.com/article/news-tp-link-router-lawsuits-fcc-ban-us/
We compare current Ring, Nest, Arlo, and Eufy outdoor security cameras by video quality, AI features, storage, subscriptions, and long-term cost.
The post Best Smart Home Security Cameras for 2026: Ring, Nest, Arlo and Eufy appeared first on TechRepublic.
https://www.techrepublic.com/article/news-best-smart-home-security-cameras-2026/
https://www.bleepingcomputer.com/
https://krebsonsecurity.com/2026/10/fbi-arrests-founder-of-ransomware-negotiation-firm/
https://krebsonsecurity.com/2026/10/shinyhunters-extorted-boeing-spin-off-prior-to-arrests/
https://krebsonsecurity.com/2026/09/u-s-soldier-gets-70-months-in-prison-for-att-verizon-extortions/
https://krebsonsecurity.com/2026/09/data-broker-radaris-loses-domains-in-privacy-fight/
I remember the name of that AI doco now - The AI Doc: Or How I Became an Apocaloptimist. I was watching it on the long-haul flight home the other day, and what I found particularly engrossing was the polar-opposite opinions from a bunch of people: "it'
I'm in Denmark! Well, just, I'm now at Copenhagen airport ready to begin the long trek home, with the final event at GOTO now done and going just perfectly. This week, there are two ShinyHunters arrests in the news: Pepijn in the Netherlands and then Saif
How's that view?! With NDC Oslo now done, it's a little bit of sightseeing before heading to Denmark for GOTO in Copenhagen for Scott's and my "Cyber-broken" talk. In the meantime, this week is mostly about the ShinyHunters trajectory targeting both
Heads up: the first 7 mins is a bit quiet until we worked out the external mic was misbehaving - sorry! But get through that and have a listen to Scott's experiences with how Report URI is identifying malware-infected machines within orgs, all due to CSP reporting. It&
I think what really resonates with me this week is being able to completely turn the tables on perceptions around things like AI being the big bad hacking tool the news would have you believe. There's the stat I talk about where it's had literally 0%
In September, hackers from a group called ShinyHunters announced that they stole a trove of FBI data about its own agents. It was an intelligence disaster.
Last week, the FBI arrested (alternate link) someone associated with that crime.
https://www.schneier.com/blog/archives/2026/10/fbi-arrests-suspect-in-fbi-hacking-case.html
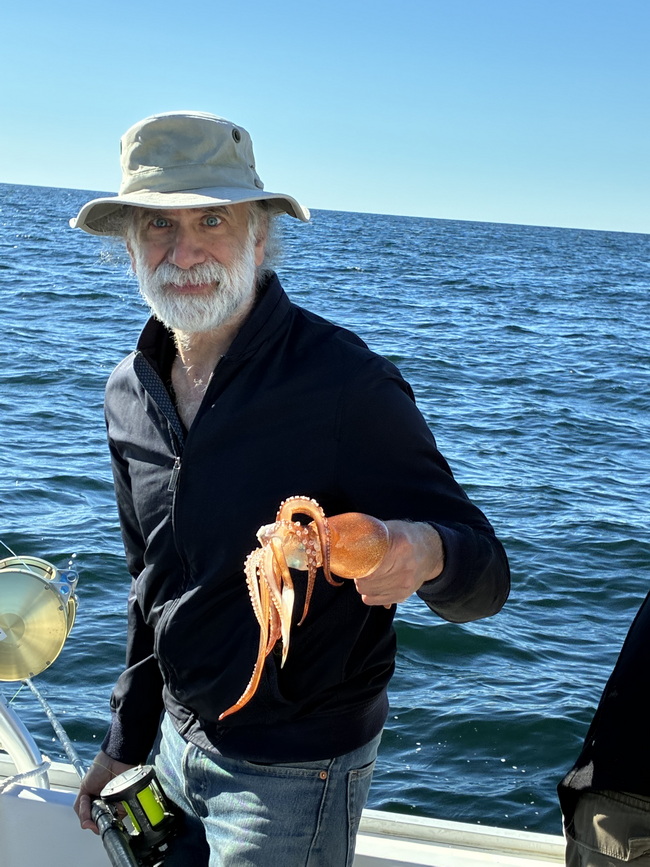
On Wednesday I spent a day fishing, on a small boat out of Gloucester, MA. We caught many cod (none of which we could keep), and a bunch of hake and mackerel (all of which we could keep). And...I caught a squid! Near as I can tell, it’s a longfin squid, sometimes called a Boston squid (Doryteuthis (Amerigo) pealeii).
That night I cooked it over a barbecue grill—hot and fast. Delicious.
https://www.schneier.com/blog/archives/2026/10/friday-squid-blogging-i-caught-a-squid.html
This essay was written with Seva Gunitsky, and originally appeared in Foreign Affairs.
Two weeks after Moscow’s full-scale invasion of Ukraine in March 2022, the Russian TV Channel One editor Marina Ovsyannikova burst onto the set of the evening newscast. She held up a hand-drawn sign behind the anchor’s head that read: “Stop the war. Don’t believe propaganda. They’re lying to you!” She shouted, “No to war!” until she was dragged away.
No one has protested the war on Russian television since then, partly as a result of tighter security and a general climate of fear. But in October 2024, Margarita Simonyan, one of Russia’s chief propagandists, gave another explanation. A growing number of the RT network’s anchors, she explained to an interviewer, are not real. “That face doesn’t exist. We generated the voice and everything else.” They were, she meant, produced by artificial intelligence. In a follow-up interview with the newspaper ...
https://www.schneier.com/blog/archives/2026/10/how-technology-empowers-and-imperils-dictators.html
Apple just released a system called “Reference Image.” It can verify the image is exactly as taken by an iPhone—new models only—without tying it to a specific iPhone or photographer. It can also verify that multiple images came from the same iPhone.
Other industry solutions require a photographer or institution to vouch for an image using their own credentials. We are concerned this puts some photographers, such as those operating in conflict zones, in a difficult position; it should not be necessary to forgo anonymity in order to prove image authenticity. We built Apple Reference Image to avoid using an explicit, public credential for photographers, and to avoid even implicit public association between different photos taken by the same sensor. The final reference image is instead signed by Apple’s signing service, after validation by PCC. That signature is backed by Apple’s strongest technical guarantees...
https://www.schneier.com/blog/archives/2026/10/apples-verified-photography-system.html
404Media is reporting (alternate link) that a cyber-weapons arms manufacturer is exploiting a vulnerability in iOS to bypass its automatic reboot security feature. This is the feature that automatically puts an iPhone into a more secure state if it hasn’t been used for 72 hours.
The new technology to get around inactivity reboot was developed by Magnet Forensics, the company behind GrayKey, a popular tool sold to law enforcement agencies that allows them to unlock and access data stored in iPhones and Android smartphones. Magnet has developed a new device called GrayKey Preserve and a feature for its regular GrayKey devices called Evidence Preservation Mode, according to the video...
https://securityaffairs.com/200832/security/canonical-hit-by-second-ddos-attack-in-2026.html